
European Sovereign Cloud Consulting and Migration Services
STX Next helps regulated European companies migrate to sovereign cloud environments that keep data under EU jurisdiction, cut hyperscaler dependency, and pass regulatory scrutiny. We’re ISO 27001 certified.
Partners




Full migration lifecycle
Assessment, architecture, execution and handover, run by one squad from the first audit through post-go-live support.

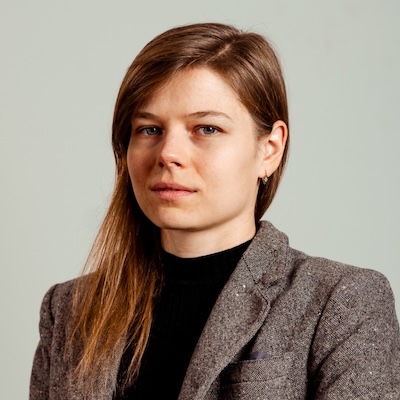
“Many executives believe that if they select the 'Frankfurt' region on a US hyper-scaler, they have solved their sovereignty issues. They haven't.”

Anna Burzyńska
Head of Cloud at STX Next

Migration assessment and roadmap
We assess your current infrastructure against your data residency requirements and produce a migration roadmap with platform recommendations, risk ratings, and a sequenced workload plan. Delivered in 2 weeks, before any architecture work begins.

Sovereign platform architecture
We design and build your sovereign cloud environment on the platform that fits your compliance profile, most often CloudFerro, STACKIT, AWS EU Sovereign, or Microsoft Sovereign Cloud. Infrastructure-as-code throughout, Kubernetes, documented security controls. Every design decision is auditable.

Migration execution and cutover
A dedicated squad, typically a Lead Cloud Architect, Cloud/DevOps engineers, and a Project Manager, manages the full migration: workload transfer, pipeline adaptation, CI/CD configuration, cutover planning, and post-migration stabilization. The team stays through go-live, then moves into a one-month hypercare period to hand off to your internal ops team.

Governance, monitoring and optimization
We configure monitoring, access auditing, and cost controls, then deliver operator runbooks and training so your team can manage the environment independently, or with light-touch support from us if you'd rather we stay close.
What problems does sovereign cloud solve?
Most organizations arrive at sovereign cloud through one of four situations: a regulatory audit, a lost deal, a legal review, or a blocked project.
Your cloud provider is subject to U.S. law, regardless of where your data sits
Our solution
Hosting data in an AWS Frankfurt or Azure West Europe region does not place it beyond U.S. jurisdiction. Both are U.S. incorporated companies and can be compelled to disclose data held anywhere in the world under the CLOUD Act. For organizations in defence-adjacent sectors, financial services, or public-sector supply chains, that exposure is a material risk. Sovereign cloud providers incorporated and operating exclusively under EU law close that gap in a way that hyperscaler "sovereign regions" structurally cannot.
EU-region hosting no longer satisfies the regulations you are subject to
Our solution
GDPR established data residency as a baseline. NIS2, DORA, and the EU AI Act are shifting focus from where data is stored to who controls it and under what legal framework. For organizations in scope, the question is no longer whether your cloud environment is compliant in principle. It is whether you can demonstrate that to a regulator who will ask.
Your enterprise customers are making it a contract requirement
Our solution
Regulated buyers in financial services, healthcare, and public administration are including cloud jurisdiction requirements in procurement terms. If you cannot demonstrate EU-sovereign infrastructure, you are losing deals to competitors who can, and you may not always know that is the reason.
Compliance uncertainty is blocking projects that should already be running
Our solution
AI initiatives, data platform builds, and analytics environments are stalled because legal or security teams cannot sign off on processing sensitive data in the current cloud environment. Sovereign cloud resolves the uncertainty and unblocks a queue of projects, not just the migration itself.
Infrastructure delivery across regulated sectors
We've migrated banking, government-adjacent, and critical infrastructure workloads from legacy and on-premise setups into compliant, scalable cloud environments.

Switzerland
Scalable, Compliant Cloud for Regulated Industries
STX Next migrated Squirro's banking and government clients from traditional VMs to Kubernetes on AWS. Regulated customers now run on infrastructure built for their compliance needs, scalable without re-architecting.
Banking & Government
Banking

Ireland
From Manual Builds to Auditable Microservices
To eliminate the daily build issues caused by manual processes, Irish financial services platform Capitalflow Group DAC migrated to a microservices architecture unified under Terraform. Today, every deployment they make is completely consistent and auditable.

Denmark
Critical infrastructure moved from on-premise to AWS with zero downtime
Polytech A/S moved critical infrastructure from on-premise to AWS with zero downtime, through a secure site-to-site VPN built for the migration. Operations now run on automated CI/CD pipelines instead of manual processes.
Critical Infrastructure
Banking

Poland
A bank's RAG system running entirely on CloudFerro
A regional European bank deployed a retrieval-augmented generation system entirely on CloudFerro, so the bank's document and query data never touched non-EU infrastructure, a common blocker for GenAI projects in banking.

Move to Sovereign Cloud with European Partner
Ready to build infrastructure that meets the highest standards for data residency and security? Get in touch with our European-based cloud architects to design a sovereign migration plan that fits your business.

ISO/IEC 27001 certified

Architecting the next standard
Real-world insights and engineering documentation from our latest Data, AI, Cloud and Software deployments.

Why STX Next?
Certified security backed by 100% EU ownership
STX Next is incorporated and headquartered in Poland, under EU law. Our information security management is independently certified under ISO 27001.
Provider-neutral across sovereign platforms
Our recommendation is based on your regulatory profile and workload needs, not which platform we'd rather sell. Beyond our core partners, CloudFerro, STACKIT, Microsoft and AWS, we build on OVHcloud or on-prem infrastructure when that's the better fit.
Open standards, so you are never locked in
Every environment we deliver runs on infrastructure-as-code and open-source tools including Kubernetes. You get full visibility into the build, and the ability to move again later without starting from zero.
Complete key control
We implement advanced encryption standards inducing BYOK (Bring Your Own Key) and HYOK (Hold Your Own Key), ensuring no cloud provider or external third party ever has access to your sensitive assets.
Upfront clarity on costs and SLAs
We eliminate surprises during the assessment phase. By conducting SLA reviews of potential providers and delivering Total Cost of Ownership (TCO) analysis, we ensure your chosen infrastructure fits your requirements and budget.
Exit strategies engineered from day one
Sovereignty isn’t complete if you’re trapped in a proprietary ecosystem. By embedding exit planning into the process, we guarantee your data and workloads stay vendor-agnostic and easy to migrate.
Talk to our Head of Cloud
Tell us what's driving the move, a regulator, a lost deal, a blocked project, and we'll assess whether sovereign cloud is the right next step.


FAQs
What is the difference between sovereign cloud and EU-region cloud hosting?
EU-region cloud hosting means your data is stored in a European data center. Sovereign cloud means the provider operates under EU law with no foreign ownership that creates extraterritorial legal exposure. AWS Frankfurt and Azure West Europe are EU-region deployments, but both companies are U.S. incorporated and subject to the CLOUD Act, which allows U.S. authorities to compel data disclosure regardless of where the data is physically stored. CloudFerro and STACKIT are not subject to that framework.
What regulations require sovereign cloud in Europe?
NIS2, DORA, and sector-specific frameworks in financial services and critical infrastructure are the primary drivers. GDPR established data residency as a baseline but does not by itself require sovereign cloud. NIS2 and DORA go further, requiring organizations to assess and manage third-country exposure in their cloud supply chains. Several national supervisory authorities have signalled that U.S.-owned providers, even in sovereign configurations, warrant additional scrutiny for regulated workloads.
What is the CLOUD Act and why does it matter for cloud migration?
The CLOUD Act is a U.S. law that allows U.S. authorities to compel American companies to disclose data they hold anywhere in the world, including in European data centers. It applies to AWS, Microsoft, and Google because they are incorporated in the U.S., which means their obligation to comply follows the company, not the data center. For European organizations processing sensitive data, this creates jurisdictional exposure that EU-region hosting does not eliminate.
AWS built AWS European Sovereign Cloud specifically to reduce that exposure. Whether it goes far enough depends on your regulatory profile, read our full breakdown before deciding. Organizations that need to remove U.S. jurisdictional exposure at the legal root typically migrate to a provider incorporated under EU law, such as CloudFerro or STACKIT.
How long does sovereign cloud migration take?
A sovereignty assessment takes 2 weeks. Architecture design takes 2 to 3 weeks after that. Migration execution then runs 2 to 8 months depending on complexity, workload count, and how many hyperscaler-managed services need open-source equivalents. A mid-sized environment typically lands at 8 to 16 weeks. After go-live, we stay for a at least 1-month-long hypercare period, usually one architect and one engineer, to transfer knowledge to your internal ops team. If needed, we’re happy to support our clients for a longer period, we also offer 24/7 DevOps support.
Can our team manage the sovereign cloud environment after migration?
Yes. Everything is delivered as infrastructure-as-code so your team has full visibility into how the environment is built. We provide runbooks, monitoring dashboards, and operator training as part of the handoff. Ongoing support is available if you want it, scoped by outcome rather than hours.
What do companies typically get wrong before starting a sovereign cloud migration?
They assume a sovereign platform is a 1:1 replacement for AWS, Azure, or GCP. It isn't always. Hyperscalers sell fully managed services, a global multi-region database with automatic failover, for example, that some sovereign platforms simply don't offer as a button you press. Some of that clustering, monitoring, and patching has to be built and run by your own team, or ours, after go-live. We scope that operational gap during the assessment so it doesn't surprise you three months into the migration.


